FCA Crypto Authorisation Gateway Sets UK Firms’ Transition Deadline
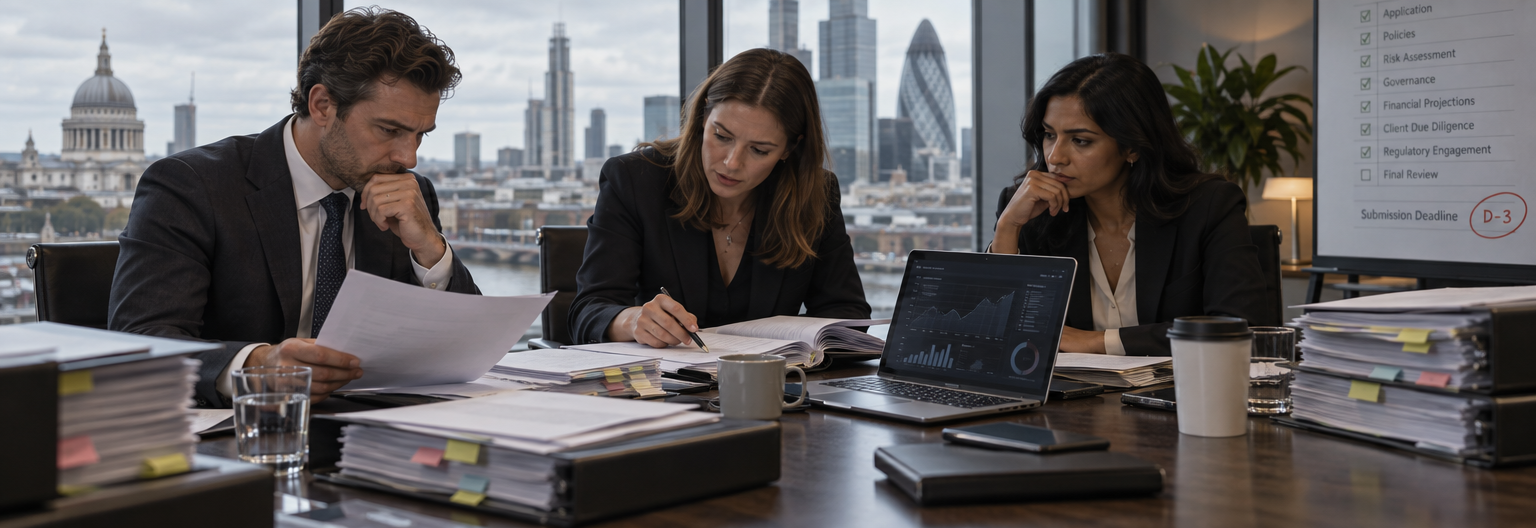
Application window is coming, but the FCA’s crypto gateway is no rubber stamp. UK firms must work out which permissions they need, prove their controls function in practice and check whether transitional rules let them keep operating. The clock is ticking; preparation, not paperwork alone, will determine who gets through.
London, England
Oct 4, 2026
The Financial Conduct Authority’s crypto authorisation gateway gives firms a defined route into the UK’s wider regulatory regime—but applying on time is only the first hurdle. Businesses will also need to establish which permissions they require, whether they qualify to continue operating during the transition and how they will demonstrate compliance.
The timetable set out in the FCA’s gateway announcement runs from 30 September 2026 to 28 February 2027, ahead of the regime’s expected commencement on 25 October 2027. For existing businesses, the application window is particularly important because it is tied to access to savings and transitional provisions while applications are considered.
Those arrangements should not be confused with approval. An eligible firm may be able to continue relevant activities pending a decision, subject to the applicable conditions. It will still have to satisfy the FCA’s authorisation requirements.
From AML registration to broader supervision
The change is more substantial than a new application form. Registration under the Money Laundering Regulations focuses on anti-money-laundering and counter-terrorist-financing requirements. Authorisation under Part 4A of the Financial Services and Markets Act 2000 brings firms into a broader framework of supervision for the activities covered by their permissions.
Existing crypto registration is therefore not a passport into the new regime. Nor should customers interpret it as equivalent to full financial-services authorisation. The FCA explains the current framework on its cryptoassets regulatory pages.
The gateway covers business models including qualifying stablecoin issuance, cryptoasset trading platforms, safeguarding and custody, and staking provision. But those descriptions are not a substitute for analysing the legal perimeter.
A business must identify what it actually does, which legal entity does it and where the activity takes place. A group offering trading, custody and staking through different subsidiaries may face several distinct permission questions. Token characteristics and the contractual relationship with customers can also affect the analysis.
The division of responsibility matters: legislation determines which activities are regulated, while FCA rules and supervision establish the requirements within that perimeter. Firms need to read both rather than work backwards from a familiar industry label.
What an application must demonstrate
The FCA has identified consumer protection, safeguarding and segregation of client assets, market integrity, and operational and financial resilience as assessment priorities. The practical implication is that firms need evidence of functioning controls, not simply a collection of policies.
For consumer protection, that means connecting disclosures to the service customers actually receive. Firms should be able to explain onboarding, charges, execution, complaints and withdrawal arrangements, including what happens when a service is interrupted. Where a business performs several roles—such as issuing a token and operating the platform on which it trades—conflicts of interest deserve particular attention.
For custody and safeguarding, the central questions concern ownership, records and control. A firm should understand how customer assets are identified and separated from its own, how records are reconciled and who can authorise movements. Key management, external custodians and procedures for responding to a security incident are part of the same assessment.
Segregation alone does not answer every question about a failure. Firms also need to understand the legal treatment of customer assets and the arrangements for returning them if the business stops operating. Marketing claims about asset protection should reflect those arrangements rather than imply guarantees that do not exist.
Trading platforms will need credible arrangements for identifying and investigating suspicious activity, managing confidential information and addressing conflicts. Resilience, meanwhile, extends beyond system uptime: funding, staffing, governance, cyber security and dependence on critical suppliers all affect whether a business can maintain services through disruption.
These are preparation priorities, not a substitute for the final requirements applicable to each activity.
The transition is conditional
The most consequential distinction is between submitting an application, qualifying for transitional treatment and receiving authorisation. They are separate steps.
Firms should not assume that an application automatically allows every existing service to continue. They need to check the eligibility conditions, the activities covered and the consequences of any refusal, withdrawal or change to their application. The commencement timetable and transitional provisions should be checked against the relevant legislation and FCA guidance as implementation approaches.
Existing obligations also remain important. The move towards a wider regime does not suspend applicable anti-money-laundering requirements or the UK’s cryptoasset financial-promotion rules.
A test of readiness—and proportionality
For firms, the immediate task is a business-wide gap assessment: map activities and entities, identify permissions, assign accountable decision-makers and establish what evidence is missing. Remediation may require changes to contracts, systems, staffing or funding well before an application can be submitted.
Smaller businesses face a sharper resource constraint. Clear expectations and proportionate evidence requirements will matter if authorisation is to distinguish well-controlled firms from weak ones, rather than simply favour applicants with the largest compliance teams. Proportionality, however, cannot mean weaker protection for customers’ assets.
The gateway provides a timetable, not a shortcut. Its significance lies in moving UK crypto regulation beyond AML registration towards scrutiny of how businesses operate. For applicants, the decisive question is whether they can demonstrate that their governance, finances and controls are suitable for the services they intend to provide.