MiCA’s Next Frontier: DeFi Gateways, Staking and Crypto Lending
Europe’s MiCA regime draws a line around crypto services. The next fight is over what happens when a company builds the doorway to decentralised finance—or stakes, lends or controls customer assets. It separates rules in force from proposals, and shows why the details could define the market’s next regulatory frontier.
Paris, France
Oct 4, 2026
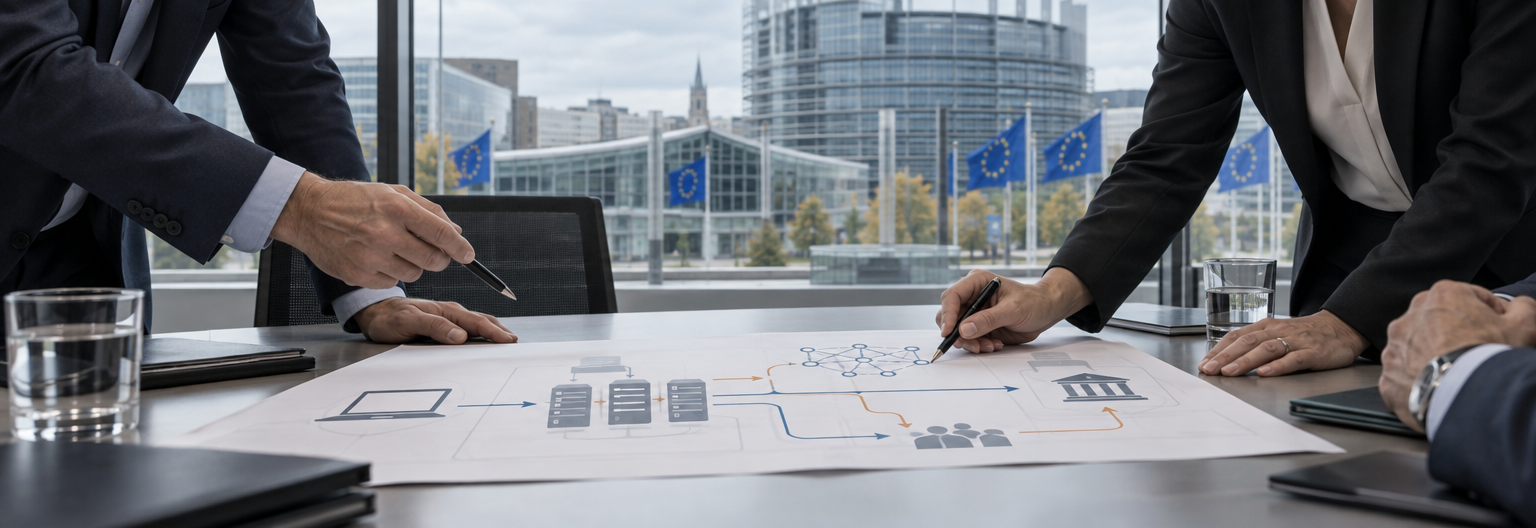
Europe’s next debate over crypto regulation concerns a boundary that MiCA has not fully resolved: when access to a decentralised protocol becomes a financial service provided by an identifiable business.
Extending the EU framework to DeFi gateways, staking and crypto lending could bring more intermediaries under common rules. But the legal distinction matters. MiCA already covers some activities conducted through decentralised technology; it does not establish a standalone authorisation category for every staking, lending or borrowing service.
The account supplied for this article attributes proposals for a broader perimeter to the European Securities and Markets Authority, citing an ESMA announcement. It dates the submissions to 30 September and 1 October 2026—after the draft’s stated reference date of 12 June 2026. Those submissions and their detailed recommendations therefore cannot be treated here as verified, completed developments. The analysis below distinguishes the reported proposals from the law already in place.
What MiCA already regulates
The Markets in Crypto-Assets Regulation, Regulation (EU) 2023/1114, became generally applicable on 30 December 2024. Its rules for asset-referenced tokens and e-money tokens applied from 30 June 2024.
MiCA regulates a defined list of crypto-asset services, including custody, operation of trading platforms, exchange, execution of orders, advice, portfolio management and transfers. Whether a business needs authorisation depends on what it actually does—not simply on whether it describes its product as DeFi.
Recital 22 draws the central distinction. Services provided in a fully decentralised manner without an intermediary should fall outside MiCA’s scope. Activities performed or controlled by identifiable persons can remain within scope even where part of the service is decentralised.
That is not a blanket exemption for businesses using smart contracts. Nor does it mean that every developer, governance participant or website operator is automatically a crypto-asset service provider, or CASP. The relevant activity must still be assessed against the regulation’s provisions.
MiCA also anticipates further policy work. Article 142 provides for examination of developments not fully addressed by the framework, including decentralised finance and crypto lending and borrowing. Reviewing those gaps is part of the regulation’s design, rather than evidence that new obligations have already been adopted.
DeFi gateways: regulating the intermediary
The reported proposal for a dedicated DeFi gateway service would target businesses that connect customers to protocols, rather than necessarily regulating the underlying code.
A gateway might select protocols, route transactions, manage a customer interface or retain powers to restrict access. Some operators also hold customer assets or control the keys needed to move them. Those functions can create an identifiable point of responsibility even when settlement occurs on-chain.
A new service category could make that responsibility clearer. Its value would depend on whether lawmakers specify which activities trigger authorisation and which remain outside the perimeter.
Publishing software is not the same as selecting investments for customers. Operating a website is not necessarily equivalent to executing orders. Holding an administrative key may be important evidence of control, but its significance depends on what the key permits its holder to do.
Legally binding decentralisation criteria could reduce inconsistent treatment across member states. Poorly drafted criteria could instead create another uncertain threshold, particularly for projects with distributed governance but concentrated operational powers.
The practical question is who controls the service, who owes duties to customers and who can be held responsible when something goes wrong.
Staking and lending need separate treatment
Staking is not one uniform business model. A customer may delegate directly to a validator, use a custodial exchange or participate in a pooled arrangement that issues a transferable token. Each structure raises different questions about custody, control, disclosures and the allocation of losses.
For intermediated staking, relevant risks include slashing, withdrawal restrictions, validator failure and unclear contractual responsibility. A proportionate regime would distinguish those risks from the separate question of whether an associated token falls under MiCA or another financial-services framework.
Crypto lending requires a different analysis. An intermediary may take control of customer assets and lend them onward, while a protocol may automate collateral requirements and liquidation. Credit exposure, collateral valuation, liquidity mismatches and the reuse of assets cannot be addressed through a decentralisation label alone.
Neither staking nor lending appears as a standalone service in MiCA’s current list. However, a business offering either may also perform an already regulated activity, such as custody or transfers. Crypto-assets that qualify as financial instruments fall outside MiCA and may engage MiFID II and other applicable financial-services rules.
Stablecoins and enforcement: precision matters
The supplied account also describes proposed restrictions on CASP services involving non-compliant stablecoins, stronger powers against fraudulent websites and crime-linked assets, and binding opinions on token classification.
These measures should not be confused with existing law. MiCA already imposes requirements on stablecoin issuers and service providers; any additional prohibition would need a precise scope, including the services covered and the treatment of existing customer holdings.
Website takedown and asset-freezing powers would require clear legal triggers, defined institutional responsibilities and avenues for challenge. Effective fraud enforcement depends on speed, but also on distinguishing criminal conduct from an unresolved authorisation or classification question.
More consistent token classification could help firms operating across borders. It would nevertheless have to respect the distinction between crypto-assets covered by MiCA and financial instruments governed by MiFID II.
What firms should do now
The immediate task for businesses is to map their activities against existing law, not assume that a reported policy recommendation has created a new licensing obligation.
That assessment should identify who holds assets and keys, who selects protocols, who controls upgrades or access, and which entity contracts with the customer. It should also separate the legal treatment of a token from the services provided around it.
A broader MiCA perimeter could strengthen customer protection and give legitimate firms a more predictable route to market. But it would require an adopted legal instrument—not merely a supervisory recommendation—and workable definitions of the activities covered.
The strongest case for reform is therefore not that everything called DeFi should be regulated alike. It is that comparable forms of intermediation should carry comparable responsibilities, while genuinely intermediary-free activity remains distinguishable from a regulated service.